Role-Based Access Control (RBAC) for Laravel. Roles, permissions and role levels. Supports Laravel 5.3 through 13.


- Features
- Framework support
- Requirements
- Installation
- Quick start
- Documentation
- Configuration
- The optional GUI
- Changing frameworks
- Artisan commands
- Screenshots
- Testing
- License
- Roles with levels, and permissions attached to roles or directly to users
- Permission inheritance from lower level roles, which can be turned off
- Entity checks, so a user can act on a model they own without a permission
- Four Blade directives and three route middleware
- Soft deletes with restore and force delete
- An optional CRUD interface in Bootstrap 4, Bootstrap 5 or Tailwind CSS
- An optional JSON API
- Every table name, model and behaviour configurable from the environment
The optional GUI ships three complete view sets. Exactly one is active at a
time, chosen with ROLES_CSS_FRAMEWORK.
| Framework | Value | Front end it expects |
|---|---|---|
| Bootstrap 4 | bootstrap4 (default) |
Bootstrap 4 CSS and JS, jQuery |
| Bootstrap 5 | bootstrap5 |
Bootstrap 5 CSS and JS, no jQuery required |
| Tailwind CSS | tailwind |
Tailwind CSS, Alpine.js, class based dark mode |
Bootstrap 4 is the default and is the markup this package has always shipped, so upgrading does not change the look of an existing install.
| Requirement | Version |
|---|---|
| PHP | 7.2 or newer |
| Laravel | 5.3 through 13 |
Continuous integration covers PHP 8.2 through 8.4 on Laravel 12 and 13.
composer require jeremykenedy/laravel-rolesThe service provider is discovered automatically.
Add the trait to the model auth.providers.users.model points at:
use Illuminate\Foundation\Auth\User as Authenticatable;
use jeremykenedy\LaravelRoles\Traits\HasRoleAndPermission;

class User extends Authenticatable
{
    use HasRoleAndPermission;
}Run the shipped migrations by turning them on:
ROLES_MIGRATION_DEFAULT_ENABLED=truephp artisan migrateOr publish them first and keep them under your own version control:
php artisan vendor:publish --tag=laravelroles-migrations
php artisan migratePublish the seeders and call them from your own DatabaseSeeder:
php artisan vendor:publish --tag=laravelroles-seeds
composer dump-autoload
php artisan db:seed
Full detail, including running the shipped seeders without publishing, is in the seeding guide.
use jeremykenedy\LaravelRoles\Models\Permission;
use jeremykenedy\LaravelRoles\Models\Role;

$admin = Role::create([
    'name'        => 'Admin',
    'slug'        => 'admin',
    'description' => 'Full access',
    'level'       => 5,
]);

$permission = Permission::create([
    'name'  => 'Can Edit Users',
    'slug'  => 'edit.users',
    'model' => 'Permission',
]);

$admin->attachPermission($permission);
$user->attachRole($admin);
Then check it:
$user->hasRole('admin');            // true
$user->hasPermission('edit.users'); // true
$user->level();                     // 5
$user->isAdmin();                   // true
$user->canEditUsers();              // true
In a view:
@role('admin')
    Only an admin sees this.
@endrole
On a route:
Route::get('/admin', fn () => view('admin'))->middleware('role:admin');Full documentation lives in the docs folder.
| Guide | Covers |
|---|---|
| Installation | Composer, the trait, migrations, publishing |
| Configuration | Every config key and its environment variable |
| Roles | Creating, attaching, syncing and checking roles |
| Permissions | Role and direct permissions, entity checks |
| Levels and inheritance | How level() and inheritance behave |
| Blade and middleware | The directives, the middleware, the exceptions |
| GUI | Turning the interface on and picking a framework |
| Artisan commands | roles:install, roles:update, roles:switch |
| API | The optional JSON endpoints |
| Seeding | The bundled seeders and how to run them |
| Testing | Running the suite and what it covers |
| Upgrading | What changed and what to do about it |
php artisan vendor:publish --tag=laravelroles-configEvery option reads from an environment variable, so most installs never edit the config file. The ones reached for most often:
| Variable | Default | Purpose |
|---|---|---|
ROLES_GUI_ENABLED |
false |
Turn the CRUD interface on |
ROLES_CSS_FRAMEWORK |
bootstrap4 |
Which view set the GUI renders |
ROLES_API_ENABLED |
false |
Turn the JSON API on |
ROLES_INHERITANCE |
true |
Inherit permissions from lower level roles |
ROLES_MIGRATION_DEFAULT_ENABLED |
false |
Run the shipped migrations |
ROLES_DEFAULT_SEPARATOR |
. |
Slug and magic method separator |
ROLES_GUI_MIDDLEWARE |
role:admin |
Who may reach the GUI |
The complete list, including every table name, model, front end asset and access control option, is in the configuration guide.
ROLES_GUI_ENABLED=trueThat registers the CRUD routes for roles and permissions, including the soft
delete dashboards. The views extend the layout named by
ROLES_GUI_BLADE_EXTENDED, which defaults to layouts.app, and your layout
needs to yield the sections the views render into:
@yield('inline_template_linked_css')
...
@yield('inline_footer_scripts')
Access is gated by Laravel's auth middleware and by role:admin, both of
which are configurable. See the GUI guide for the full route
list and access control options.
After installation, use update or switch to change the CSS framework without losing configuration.
php artisan roles:updateOr pass the option directly:
php artisan roles:update --css=bootstrap5| Option | Values | Description |
|---|---|---|
--css |
bootstrap4, bootstrap5, tailwind |
Change the CSS framework |
php artisan roles:switch --css=tailwindIf you published the views, republish them for the framework you moved to:
php artisan vendor:publish --tag=laravelroles-views-tailwind --force| Command | Description |
|---|---|
roles:install |
Fresh install with interactive prompts. Detects an existing installation. |
roles:update |
Change the framework interactively. Does not overwrite config or published views. |
roles:switch |
Quick framework change from a flag. |
| Flag | Description |
|---|---|
--css= |
CSS framework: bootstrap4, bootstrap5, tailwind |
--force |
Skip the reinstall confirmation when already installed |
Passing --css skips the prompts, so the commands work unattended in a deploy
script. Full detail in the commands guide.
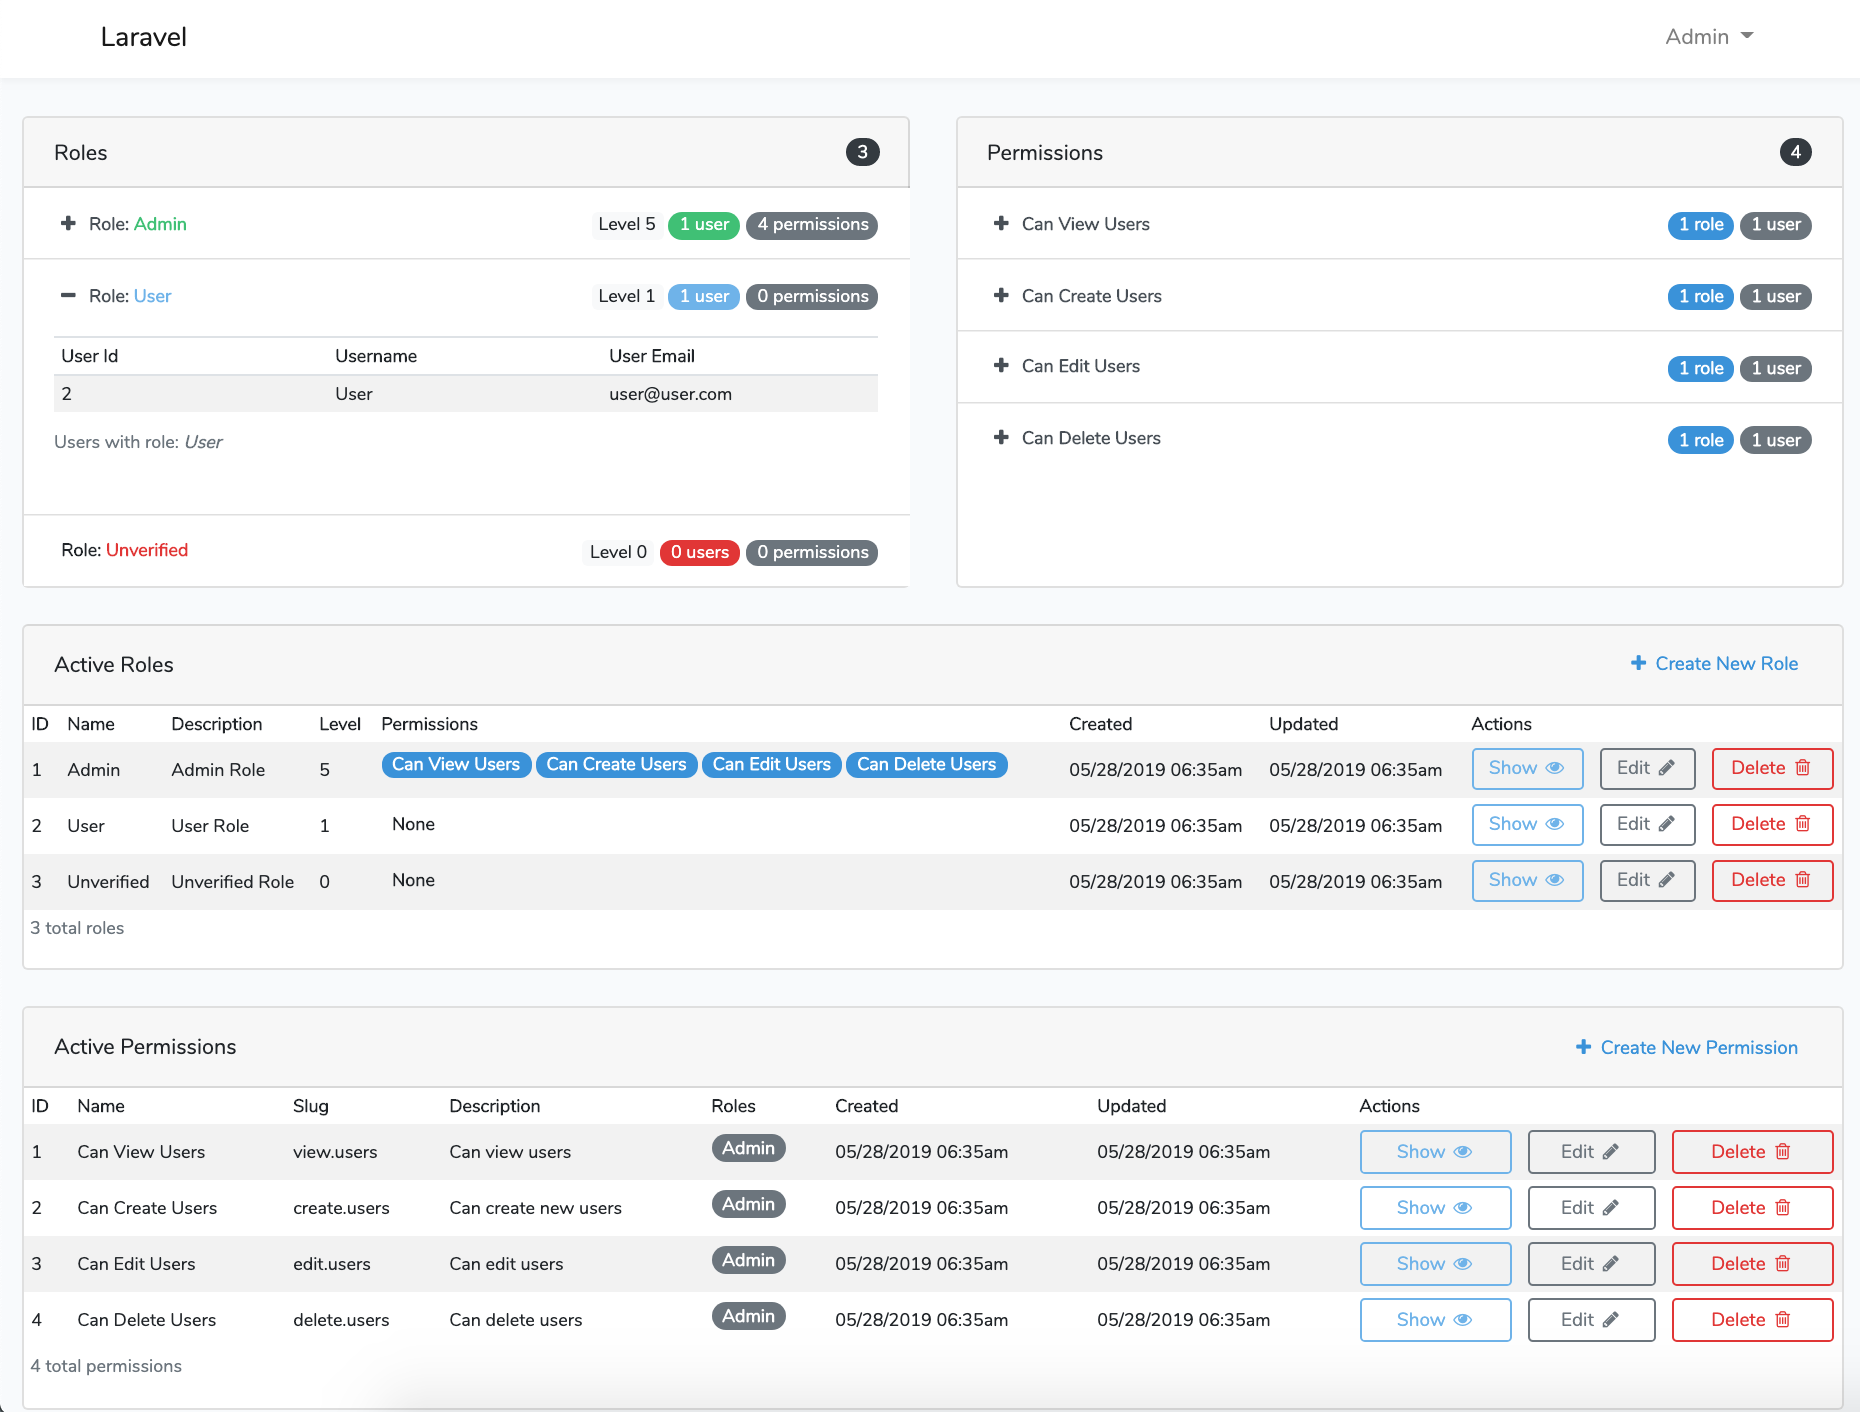
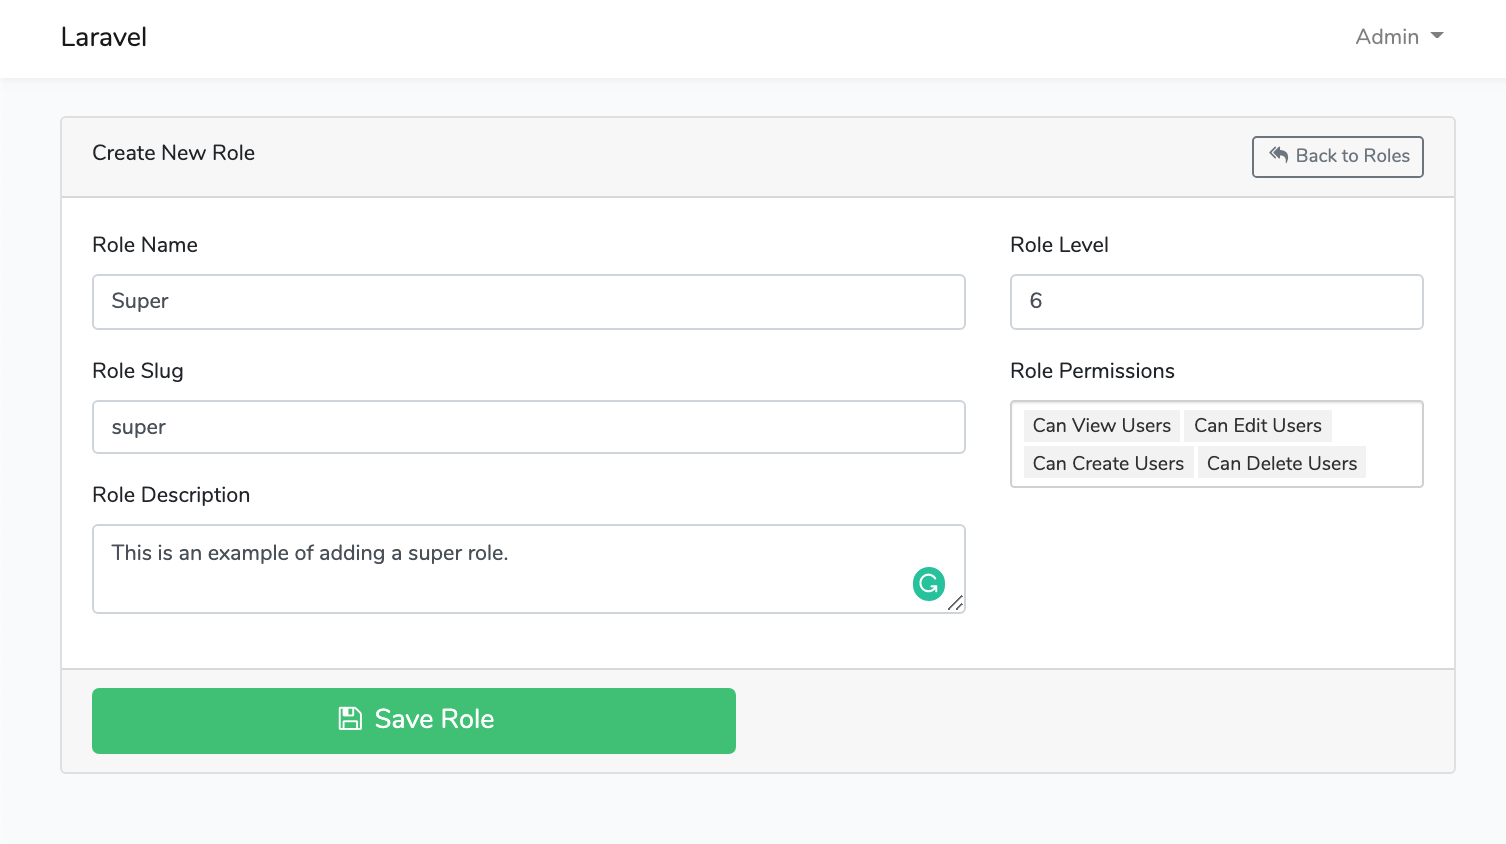
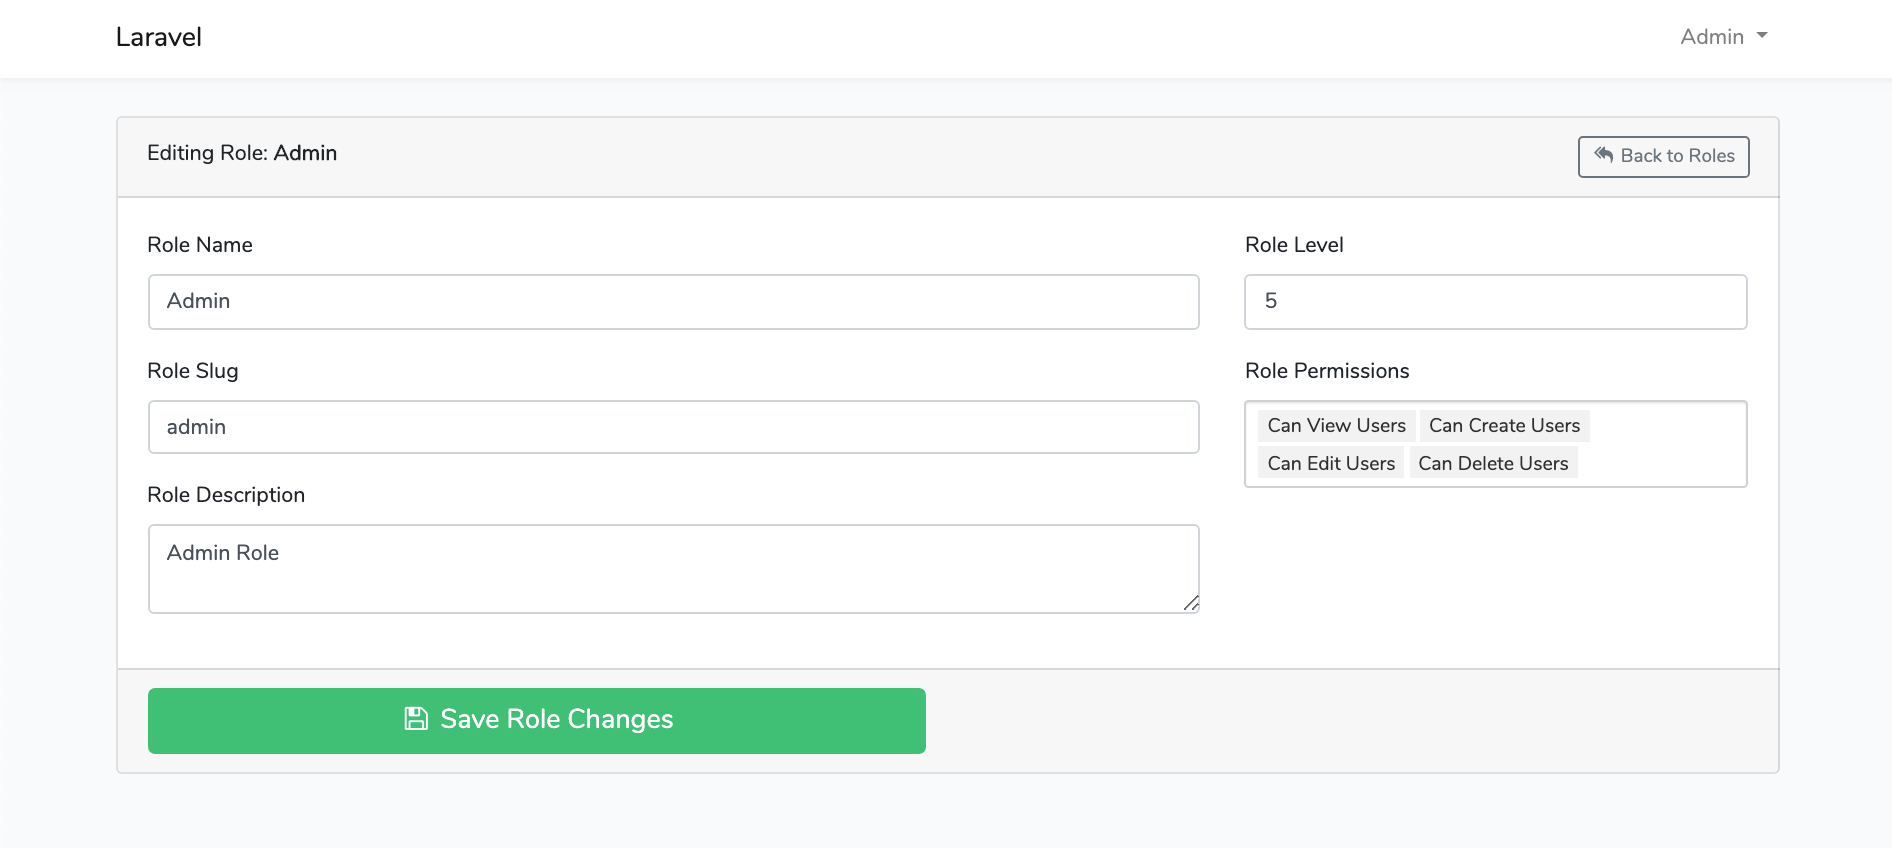
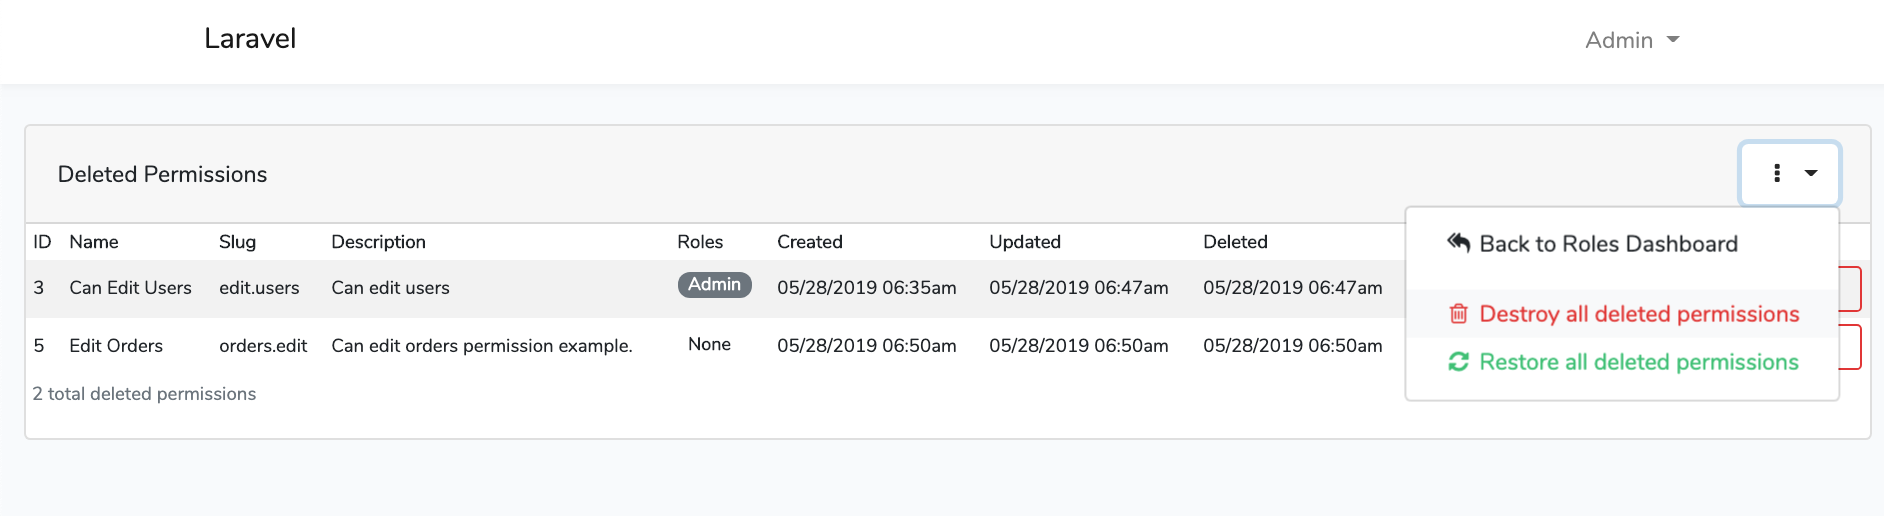
These show the Bootstrap 4 interface.
| Roles dashboard | Create a role |
|---|---|
 |
 |
| Edit a role | Role detail |
|---|---|
 |
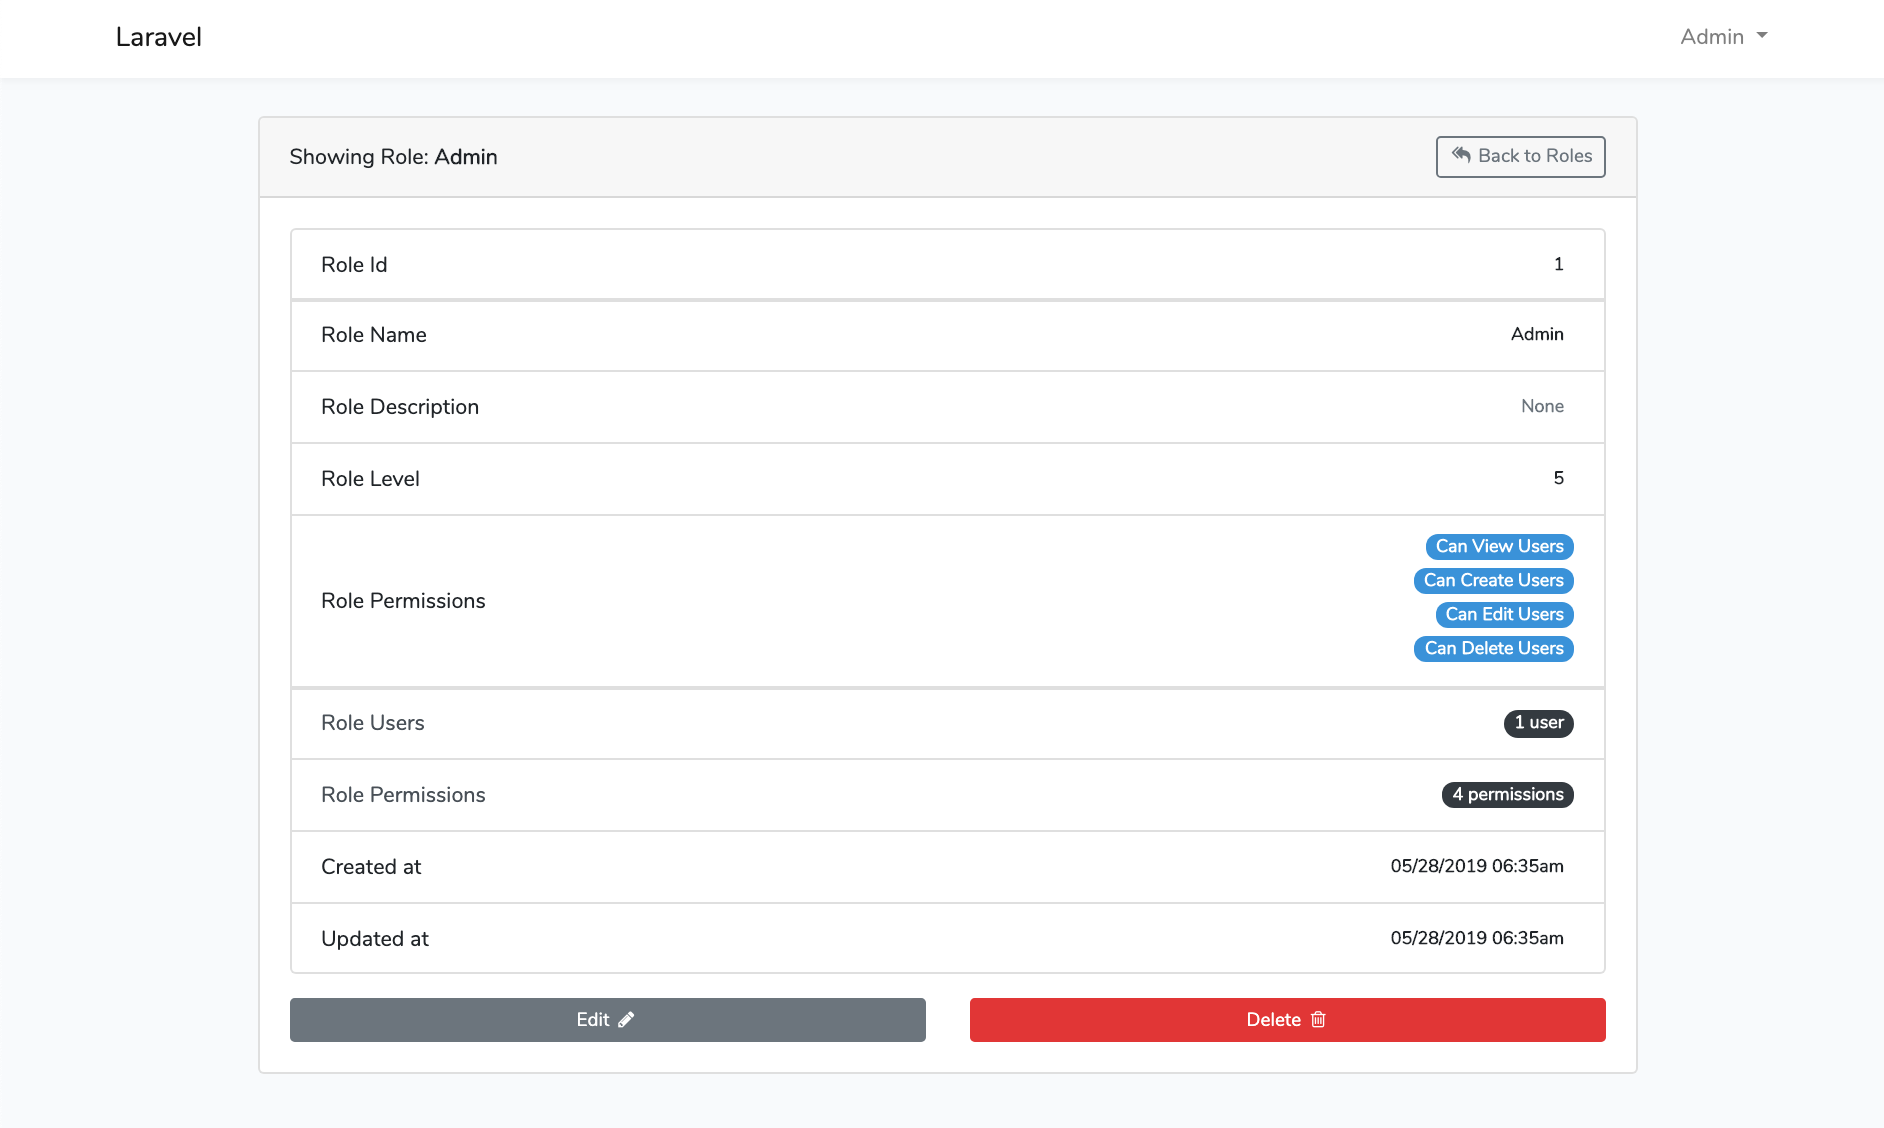 |
| Delete a role | Deleted role detail |
|---|---|
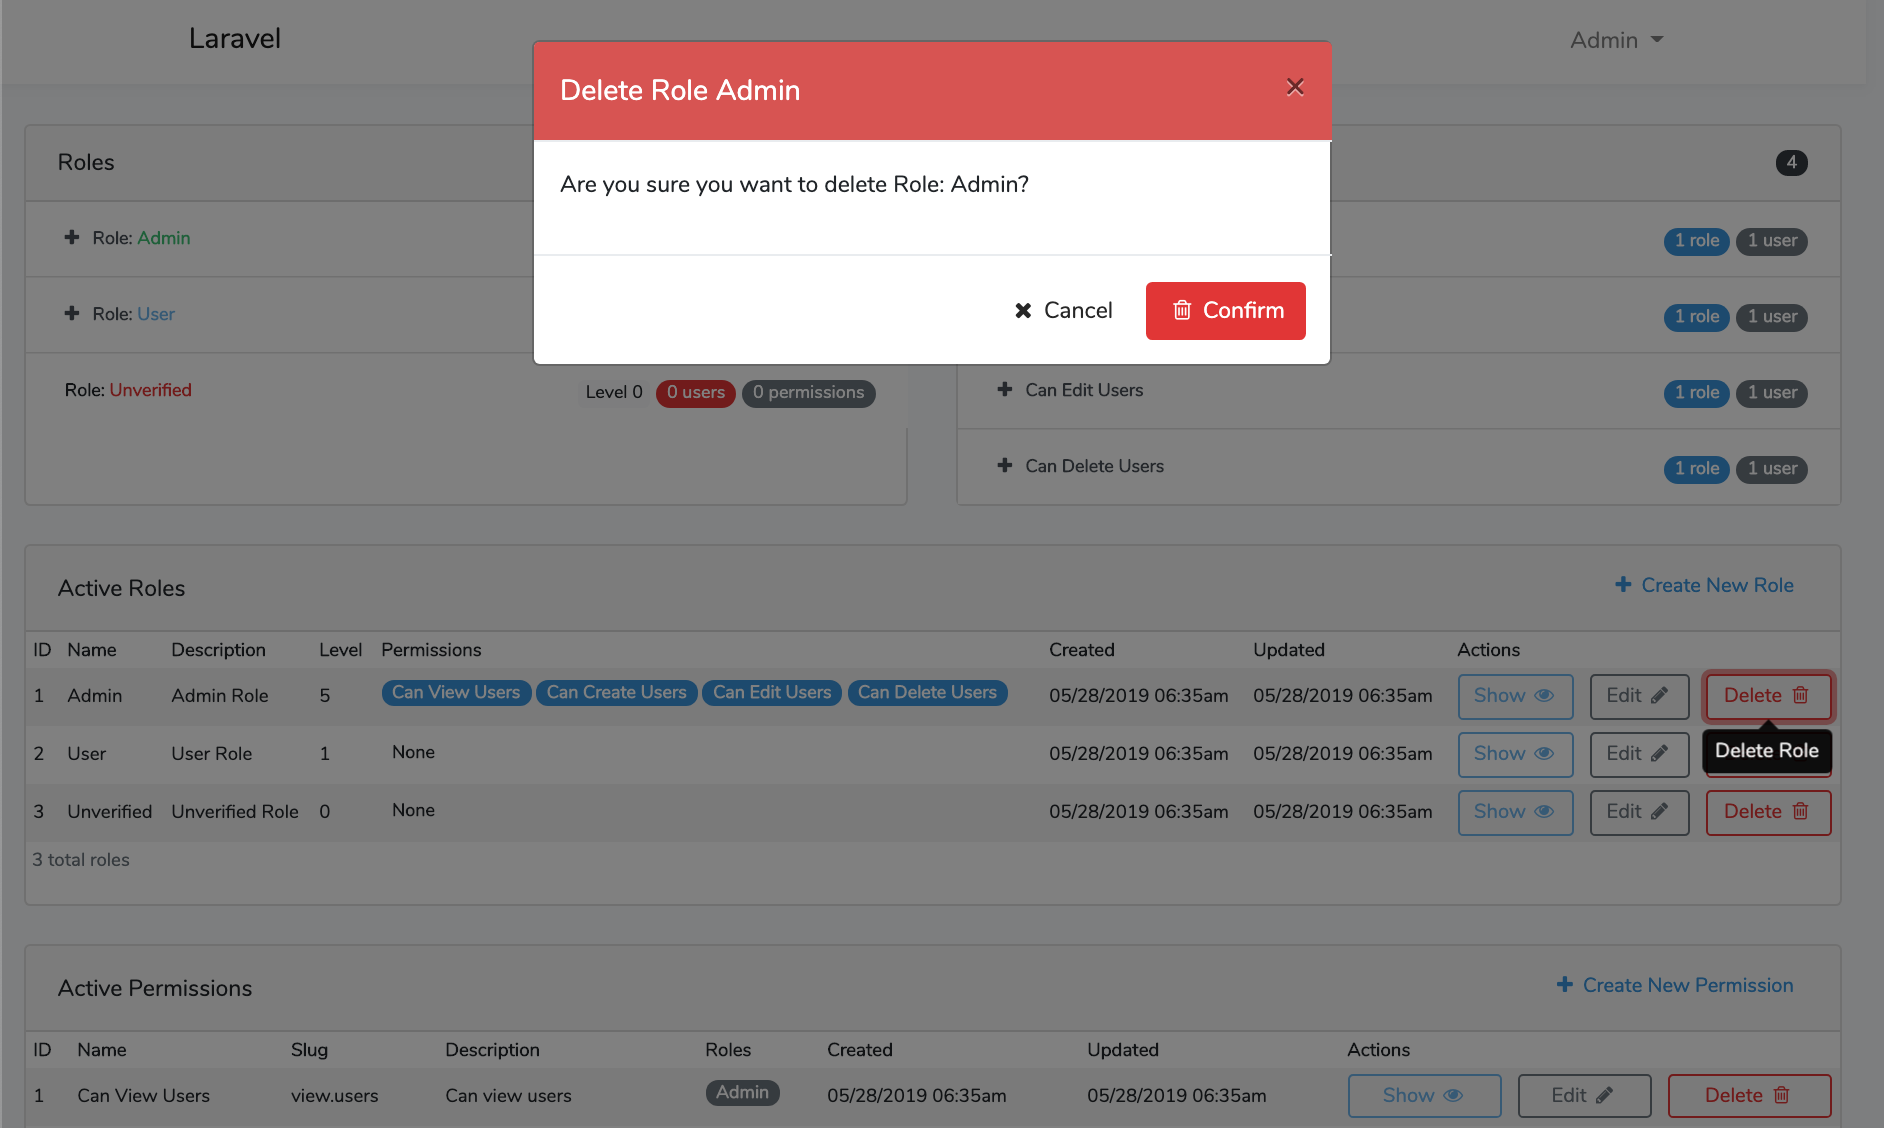 |
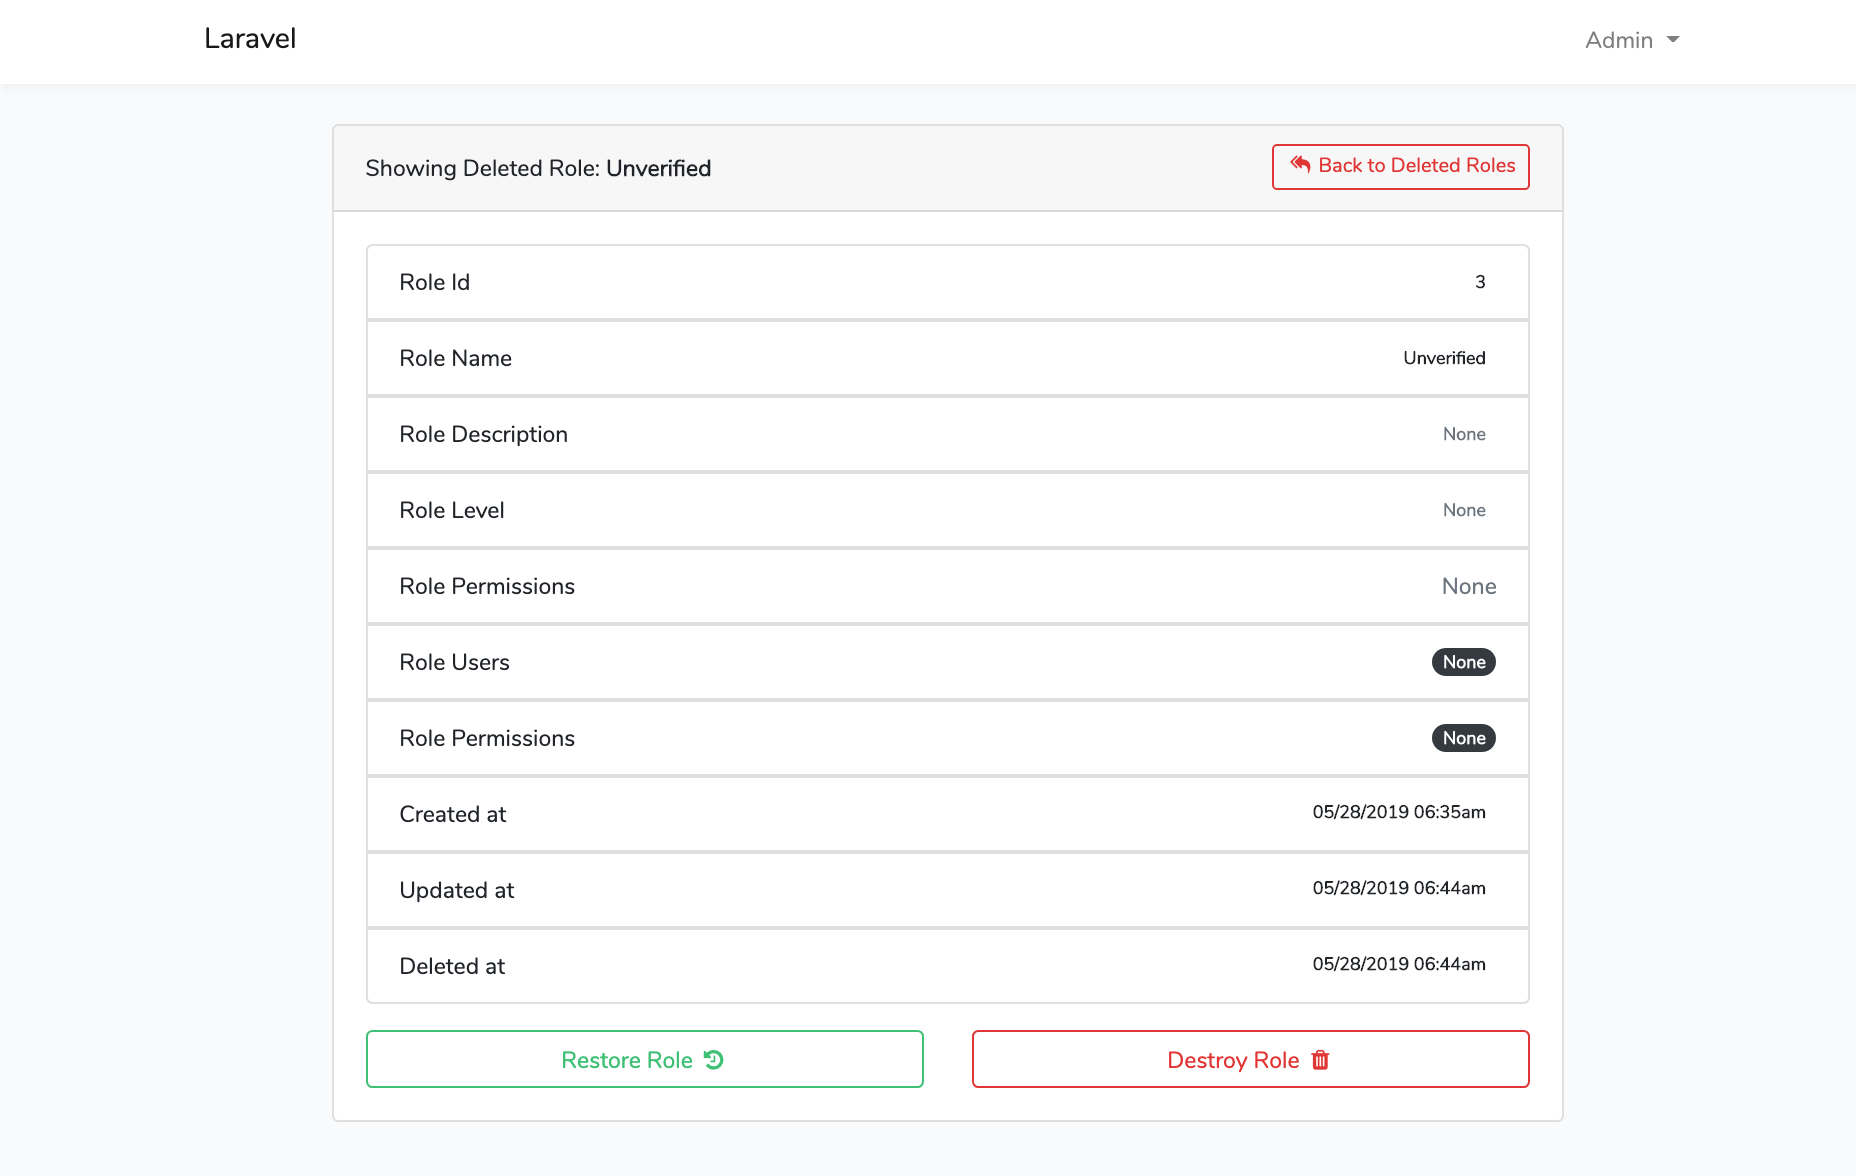 |
| Restore a role | Deleted roles dashboard |
|---|---|
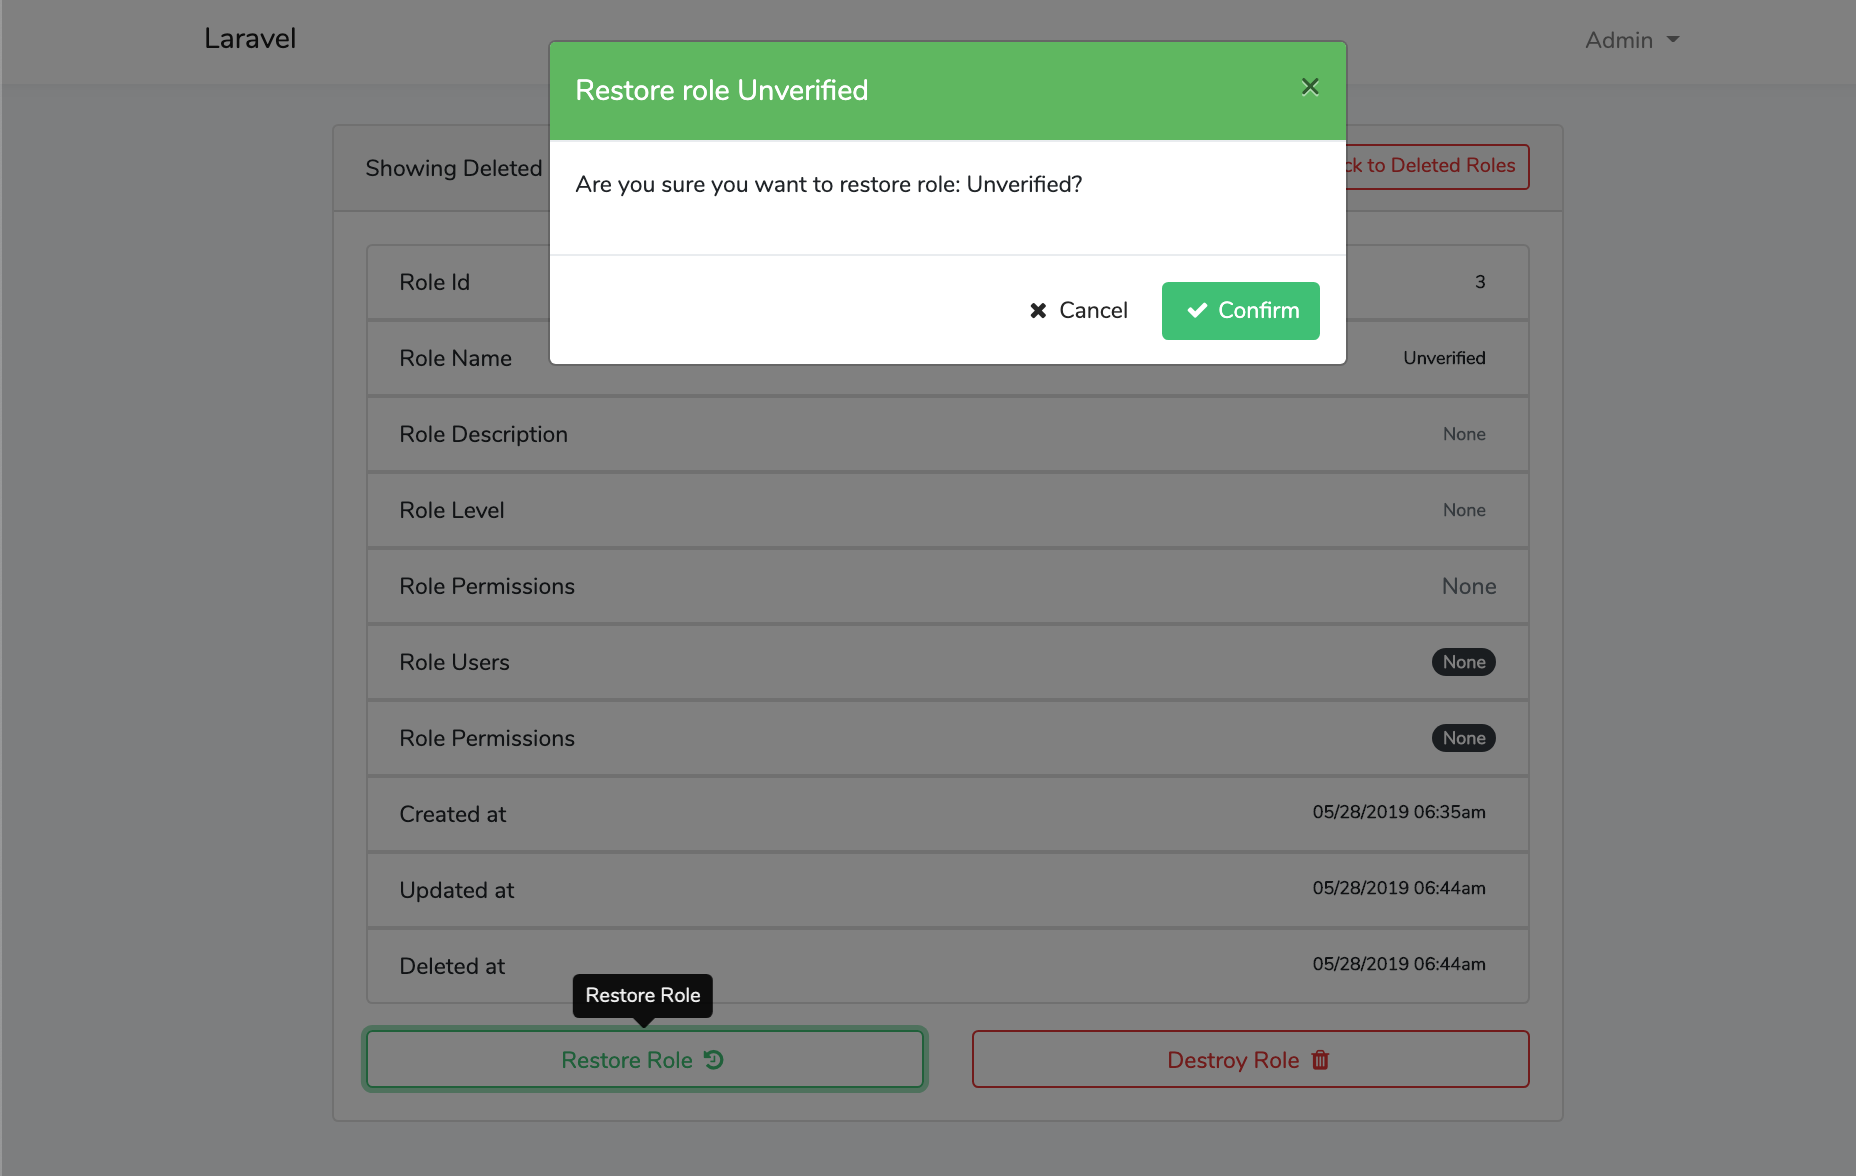 |
 |
| Permissions dashboard | Create a permission |
|---|---|
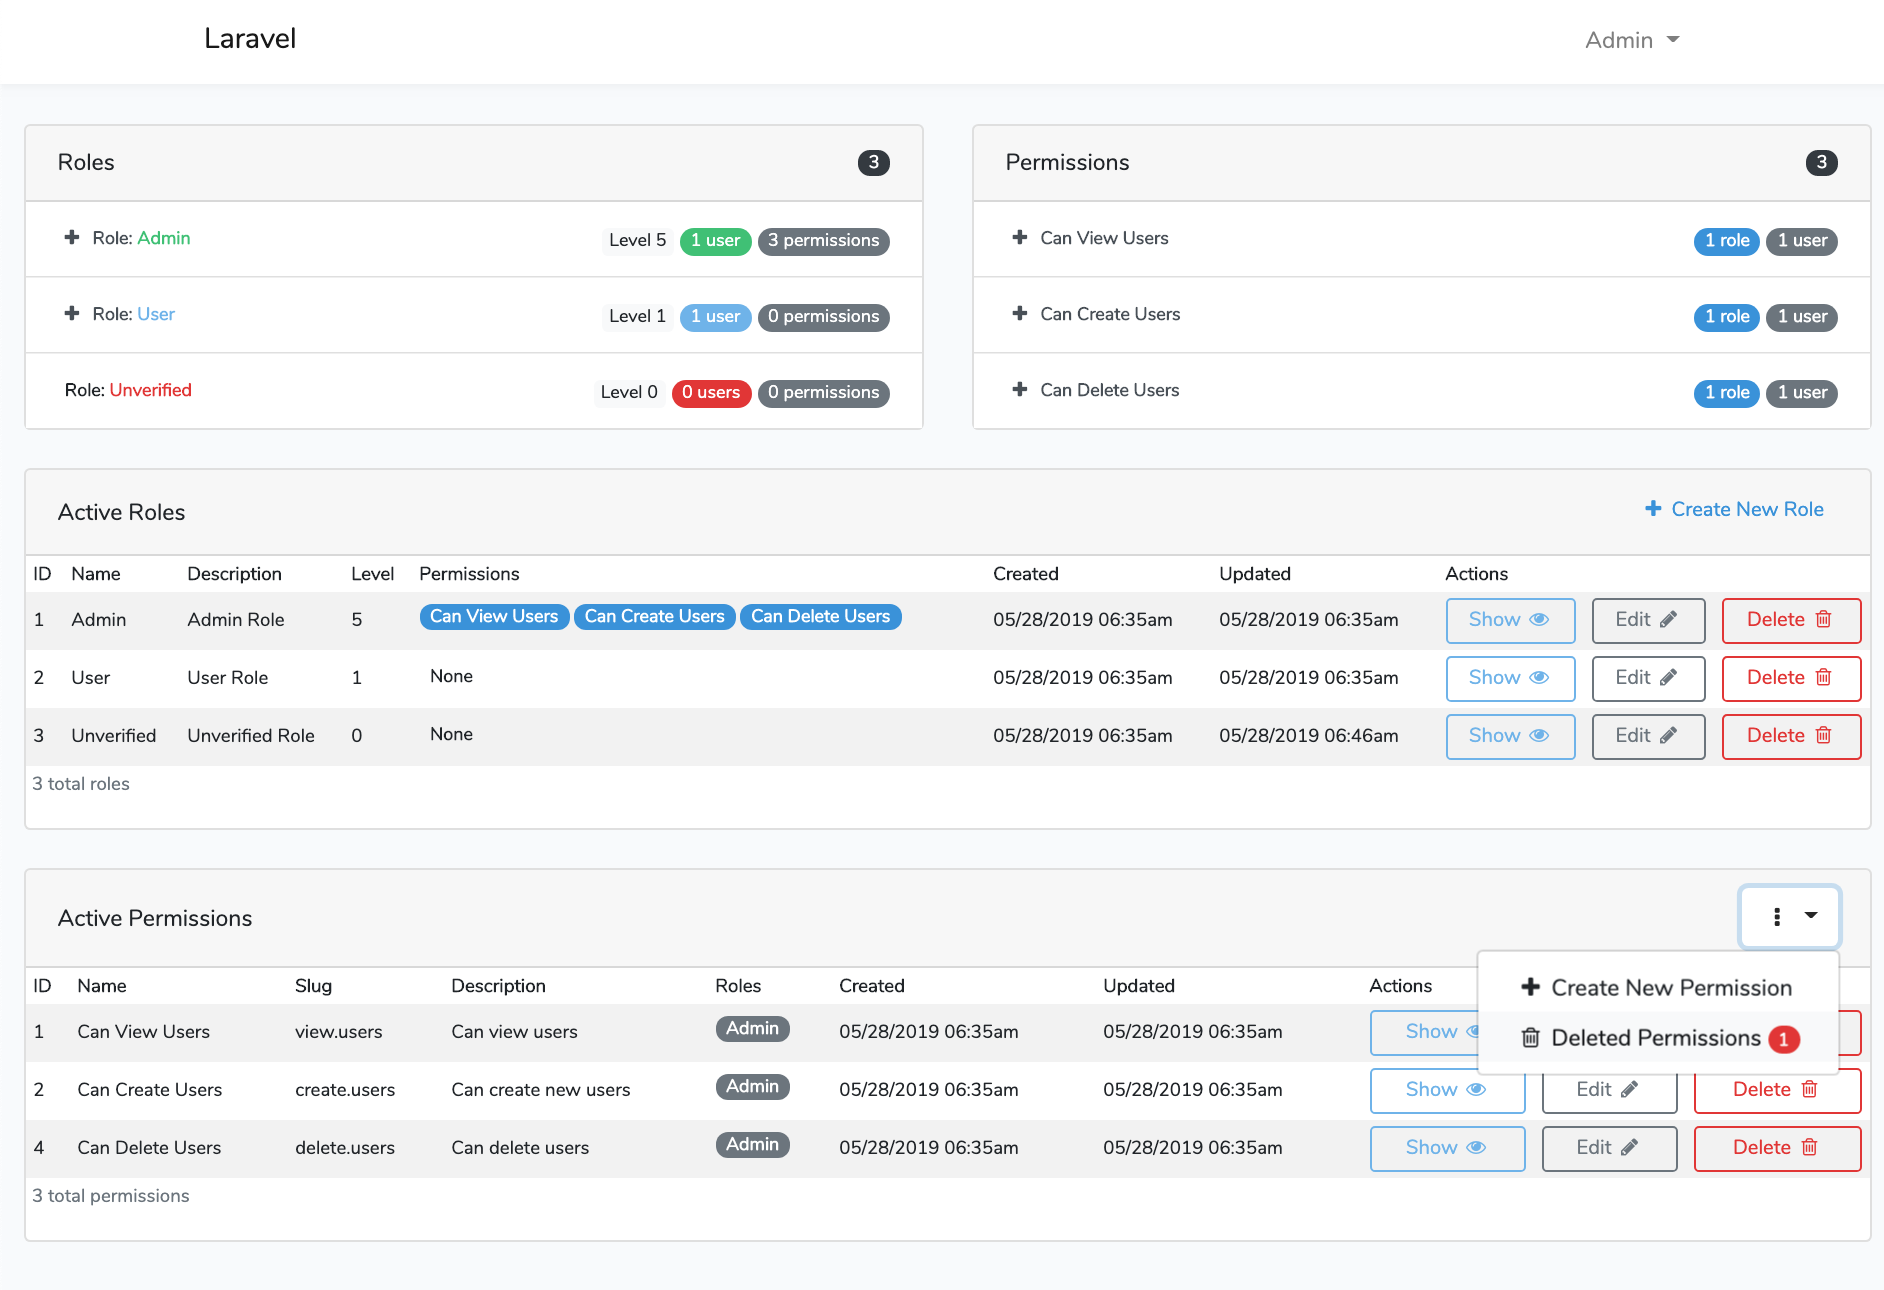 |
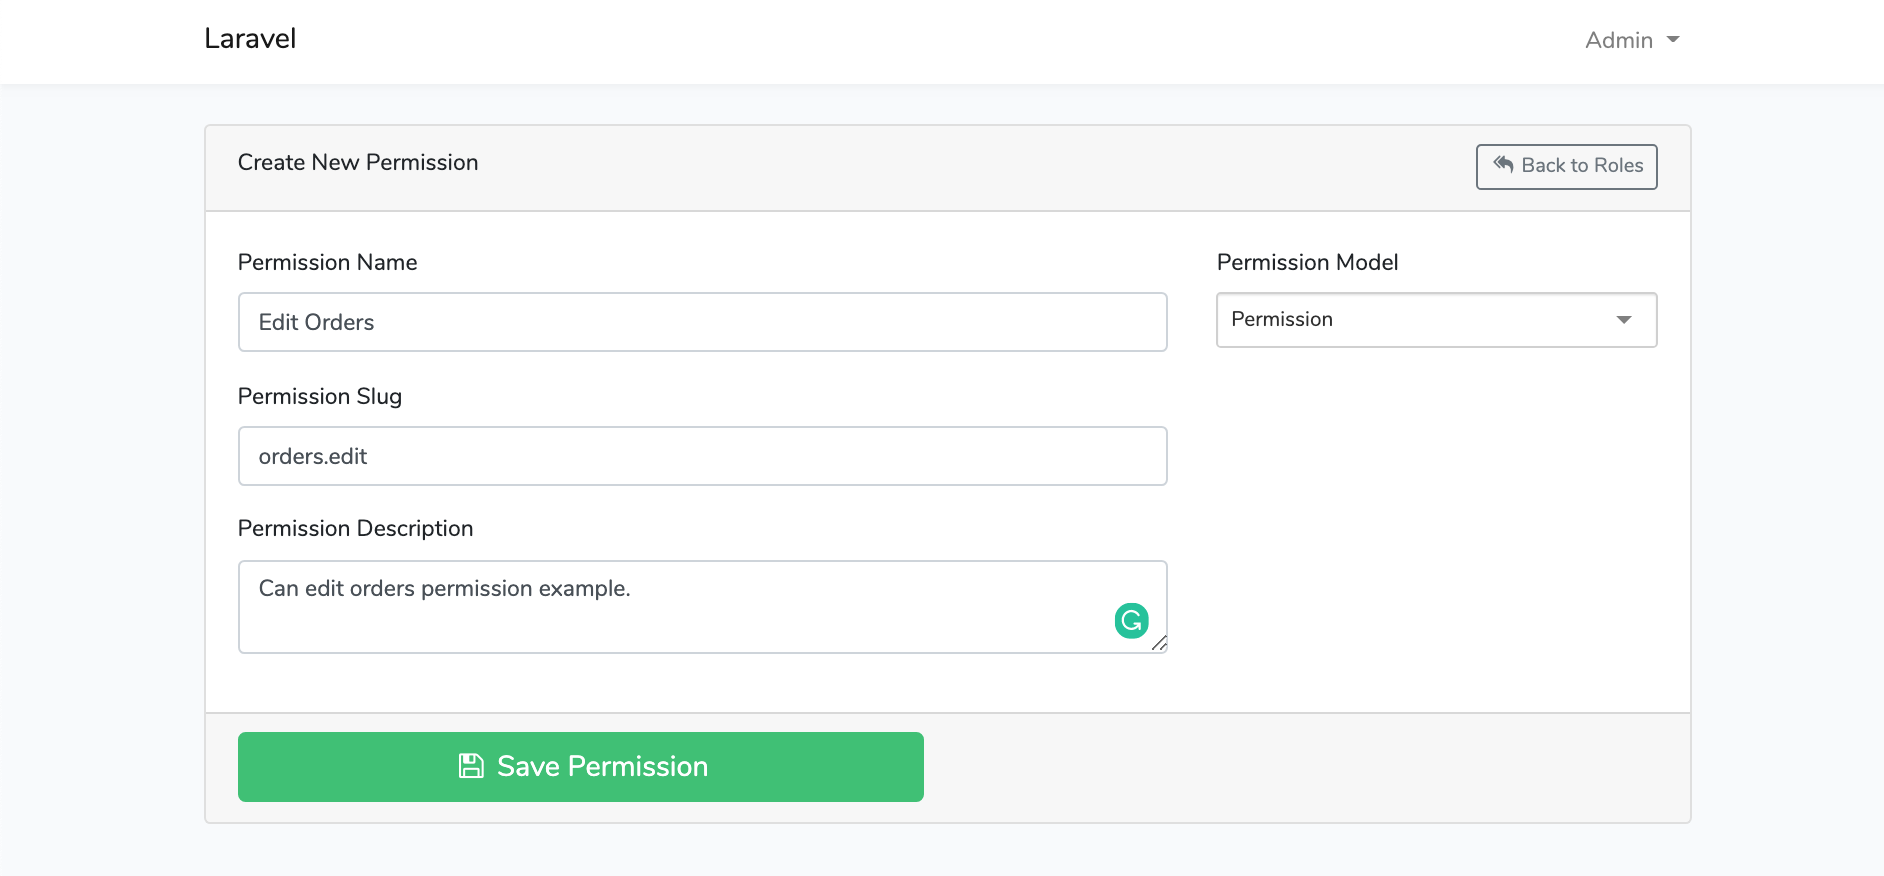 |
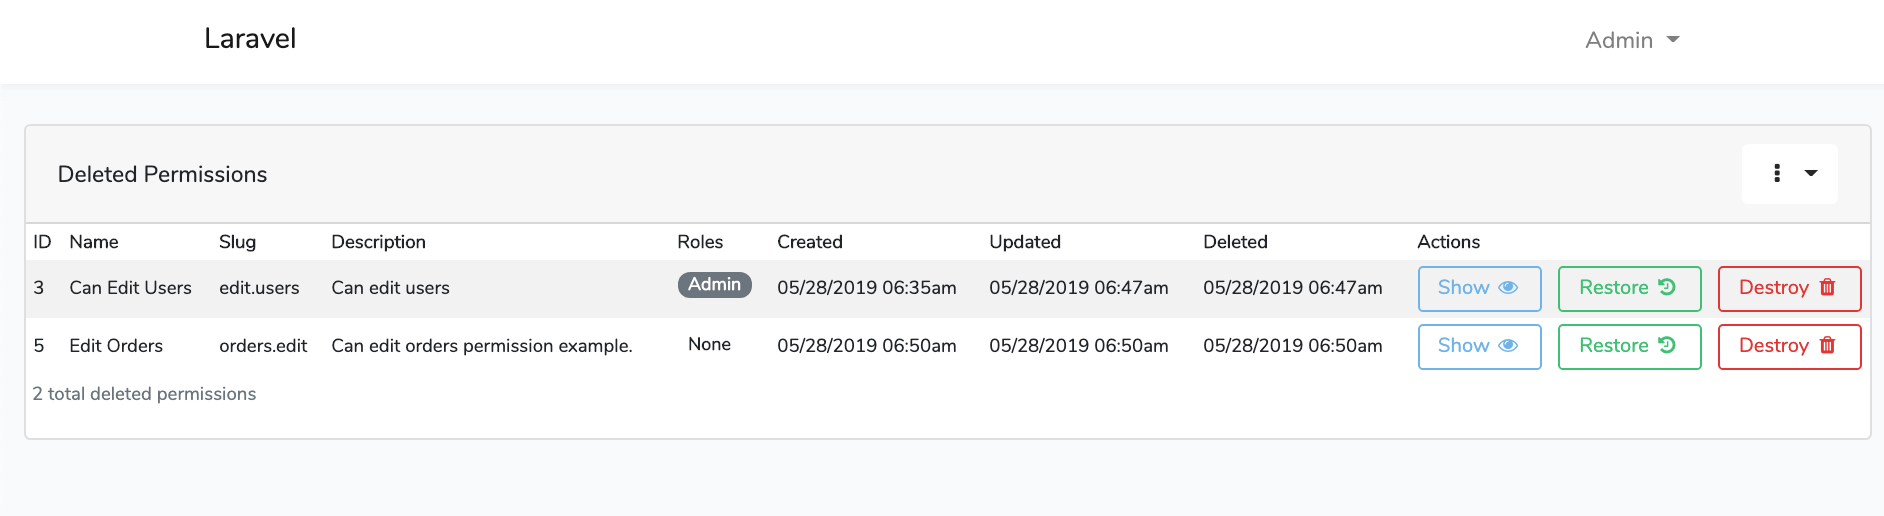
| Permission detail | Deleted permissions dashboard |
|---|---|
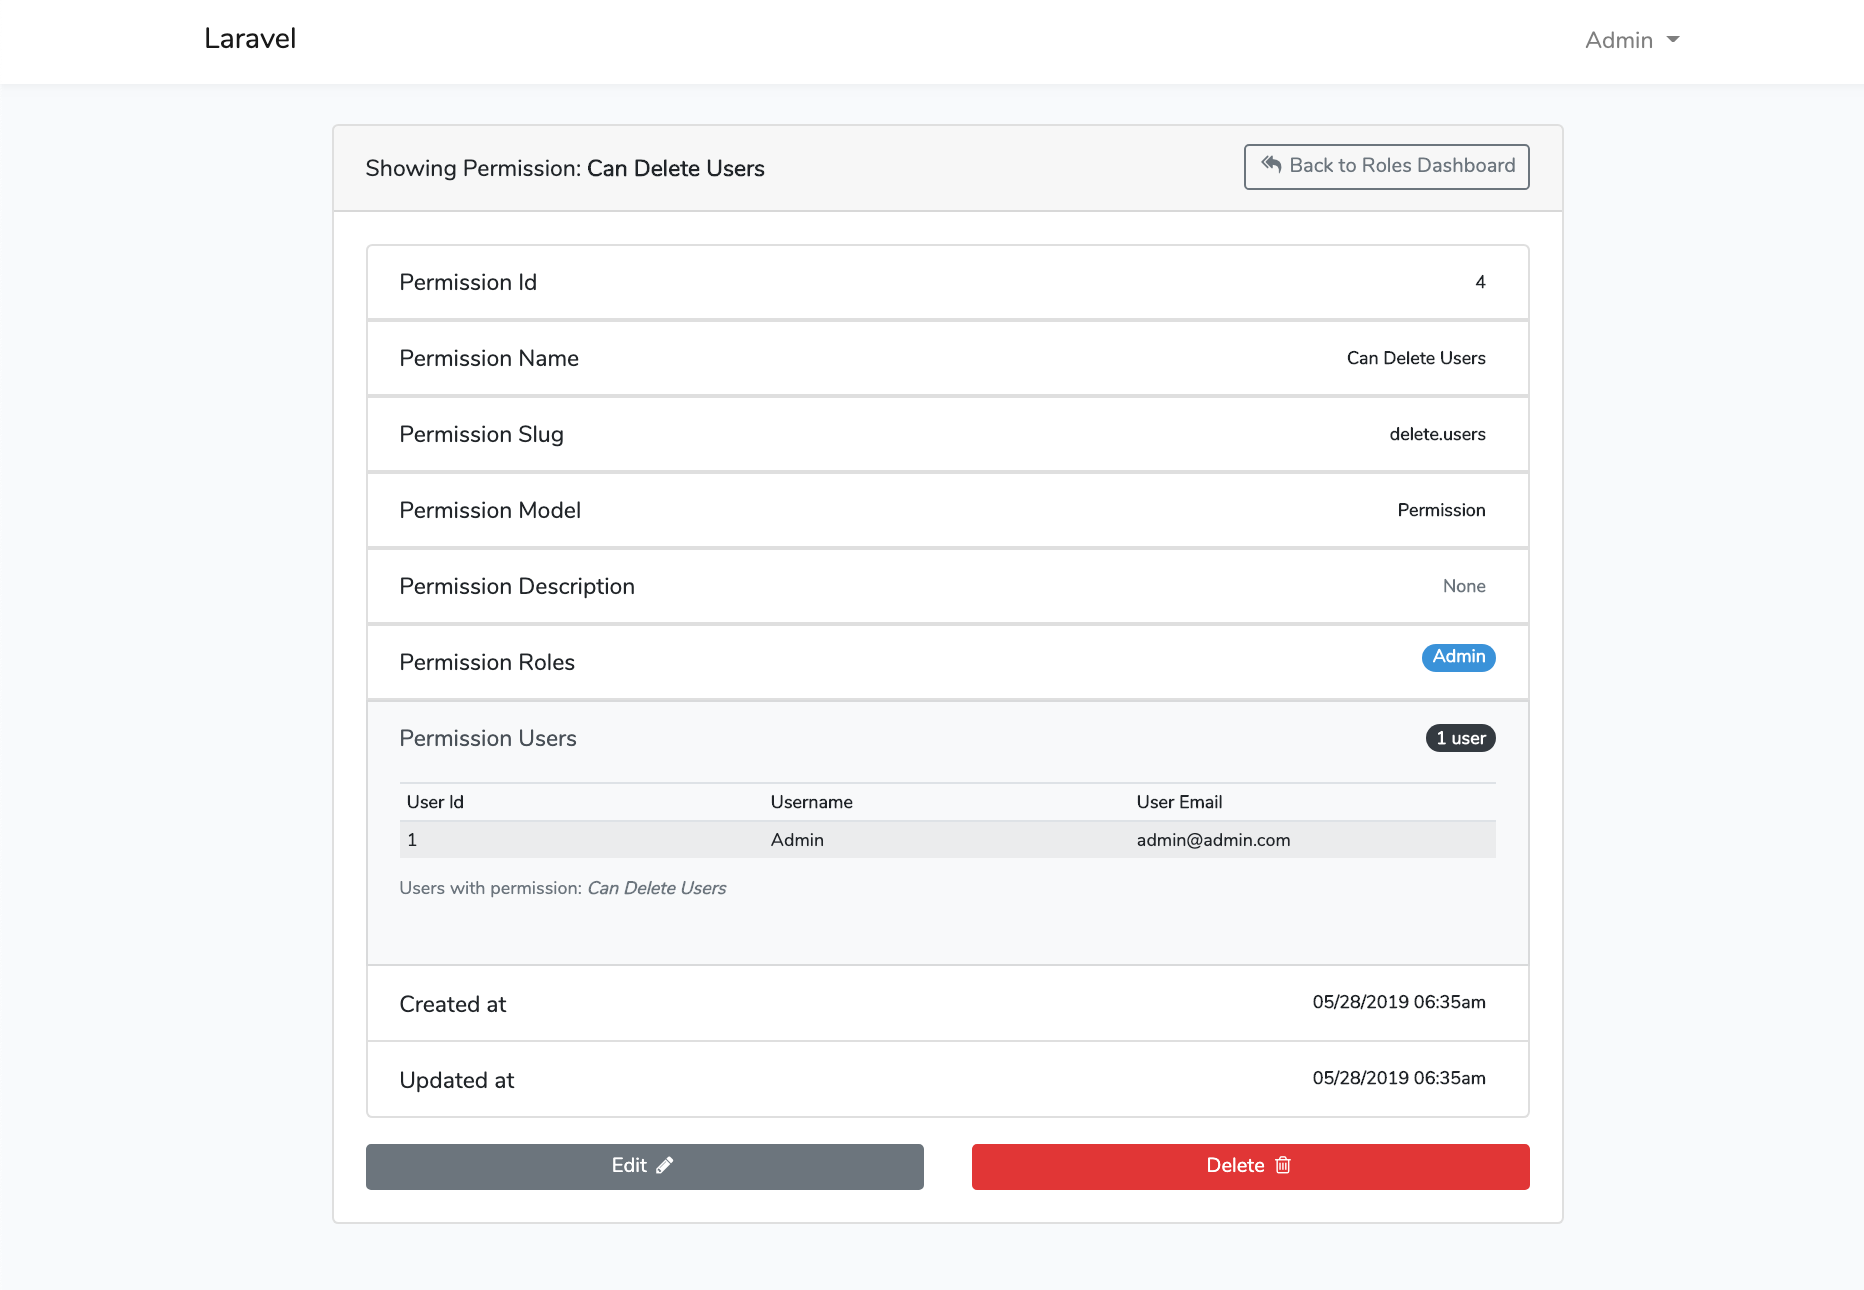 |
 |
composer test
composer lint
See the testing guide for what the suite covers.
This package is open-sourced software licensed under the MIT license.